 Aller au contenu


Bare Metal Provisioning: How Servers Are Deployed in Minutes
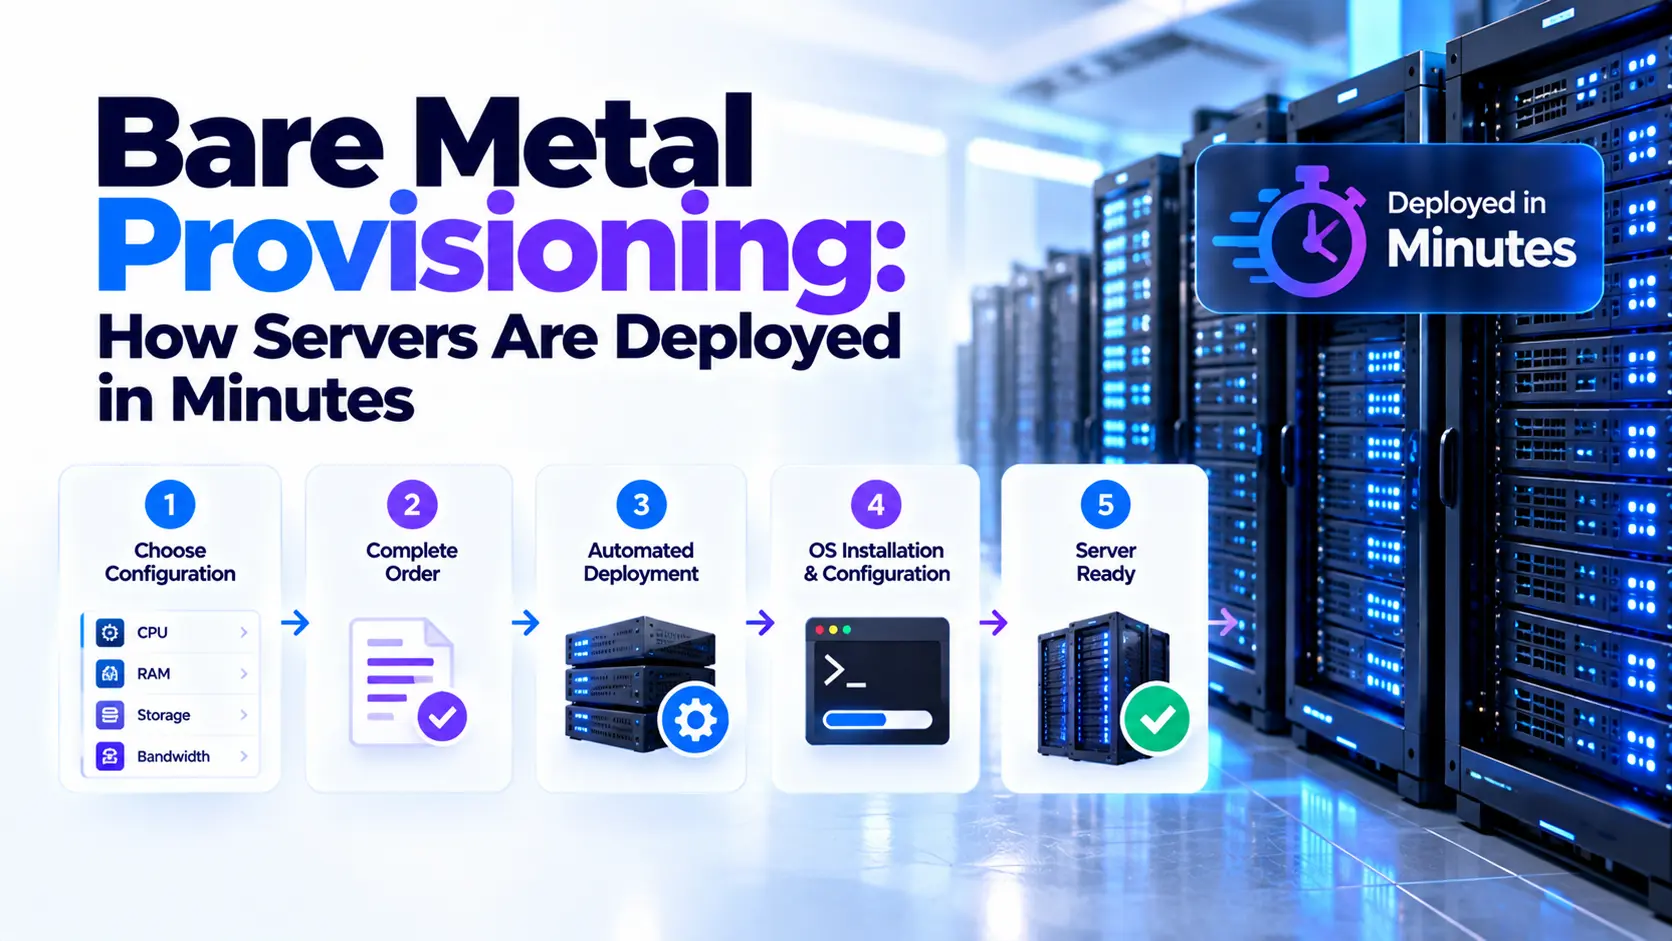
Bare metal provisioning prepares a physical server for use by assigning hardware, setting up storage and networking, installing an operating system, and configuring access. Deployment can take minutes when the hardware is already installed, checked, and available, and software handles the remaining steps.
The delivery claim still needs a clear finish line. A server that accepts an SSH connection may need more configuration before it can run your application.
In this guide, we explain what happens between a server request and a usable machine, which tools handle the work, and what to check before planning around a delivery estimate.
What Is Bare Metal Provisioning?
Bare metal provisioning turns physical server resources into an environment ready for an agreed task. The process can involve manual work, automation, or both.
It commonly includes:
- Assigning a server with the required CPU, memory, and storage.
- Applying the storage layout and boot settings.
- Installing an operating system or a type-1 hypervisor.
- Connecting the server to the correct networks.
- Setting up authorized access.
- Checking that the delivered system matches the request.
A bare metal server can arrive with an operating system already installed. The term describes the physical computing environment, not a requirement to receive an empty disk.
Provisioning, Configuration, and Application Deployment
These activities overlap, but they have different outcomes.
| Activity | Main purpose | Example |
|---|---|---|
| Provisioning | Prepare the requested infrastructure | Assign a physical server and install Linux |
| Configuration | Apply the settings needed for its role | Set firewall rules and configure storage mounts |
| Application deployment | Install and start the workload | Run a database service or game server |
We should agree on the expected handoff before comparing delivery times. An OS installation and a completed database migration are different jobs.
How Can a Physical Server Be Deployed in Minutes?
Fast deployment depends on preparation completed before the request and automation applied after it. The physical work still exists, even when the customer does not wait for it.
Work Completed Before the Order
A provider can maintain a pool of servers that already have:
- Rack space, power, and network cabling.
- Recorded hardware specifications and asset identities.
- Working remote-management access.
- An approved firmware state.
- Completed hardware checks.
- Storage cleared according to the provider’s reuse policy.
- Access to supported installation images.
These machines can wait for allocation without requiring a technician to install new parts for each order. They do not all need to remain powered on.
Canonical’s MAAS machine lifecycle illustrates this separation: hardware preparation and inspection precede allocation and deployment.
Work Triggered by the Order
Once a suitable machine is available, automation can reserve it, select a boot method, apply the requested storage layout, install the OS, and set network and access details.
A standard configuration reduces the number of decisions during the job. A supported image and a known disk layout also reduce the need for manual intervention.
Conditions That Change the Timeline
A custom GPU configuration, unavailable storage device, new network connection, or unsupported OS image can move the request outside the standard process.
Payment review, capacity queues, and account checks may also affect the time from order to access. Ask whether those steps form part of the quoted estimate.
What Does the Provisioning Timer Measure?
A useful delivery estimate states when the clock starts and what must work before it stops.
| Measurement | Start point | Finish point |
|---|---|---|
| Customer delivery time | Order submission or approval, as stated | Agreed customer handoff |
| Allocation time | An eligible request enters the allocation process | Matching hardware is reserved |
| OS provisioning time | The deployment job starts | The installed OS passes its readiness checks |
| Workload readiness time | The agreed request or job begins | The application passes its health check |
For example, IBM’s Bare Metal Servers for VPC page advertises provisioning within ten minutes when resources are available. Servers.com’s provisioning documentation states delivery from fifteen minutes when the ordered configuration is already in the rack, with longer timelines when hardware or configuration changes are needed.
These statements describe different services and conditions. They do not form a direct performance comparison.
We also need to separate elapsed time from individual task durations. Some tasks can overlap, while others must wait for earlier work to finish. Adding every task duration may therefore produce a different number from the customer’s total wait.
For planning, ask for typical results, failed-job handling, and the conditions behind the estimate. A single fastest run tells us little about a busy period or a different configuration.
The Bare Metal Provisioning Process, Step by Step
The exact sequence depends on the platform. A typical workflow moves through the following stages, with checks at each handoff.
1. Check the Request and Reserve Matching Hardware
The request defines the location, CPU, memory, storage, operating system, and network requirements. It may also include GPUs, a RAID layout, private-network membership, and an SSH public key.
The platform checks available inventory and reserves a matching host. A successful API response may only confirm that the request entered a queue. It does not necessarily mean a physical server is ready.
A job ID lets the customer or automation system follow the request without submitting it again. If the first request times out, check its status before retrying and creating another billable server.
2. Check Hardware Health and Configuration
The platform checks that the selected machine has the expected components and can support the requested installation.
This can include disk health, network interfaces, firmware state, and BIOS or UEFI boot settings. Some checks happen during earlier commissioning. Others must run again after hardware changes or a failed job.
Firmware updates do not need to run on every order. Applying an approved baseline before allocation can reduce deployment work, provided the platform still checks that the machine meets the current requirements.
3. Set Power and Boot Options
A baseboard management controller, or BMC, provides a hardware-management path separate from the installed OS. It can support actions such as power control, console access, and boot selection.
DMTF Redfish and IPMI provide management interfaces used by automation systems. Available functions depend on the server, firmware, and platform integration.
For practical background, our IPMI and out-of-band management guide explains this separate access path.
OS administrator access does not automatically grant BMC access. Check how the provider supplies and protects each one.
4. Load the Installer or Deployment Agent
The server needs a way to start the installation environment. Common options include network boot and remote virtual media.
PXE can start a network boot process. iPXE adds boot capabilities such as retrieving files through HTTP and using scripts to select the next action. Supported firmware may also offer UEFI HTTP boot.
Another workflow can mount installation media through the management controller. The right method depends on hardware support and network design.
We should avoid treating PXE as a requirement for every bare metal platform. Different boot paths have different dependencies and failure points.
5. Prepare Storage and Install the OS
The installer or deployment agent identifies the correct target disks, applies the requested layout, and writes the operating system.
Storage preparation may include RAID, partitions, filesystems, and bootloader setup. The platform must distinguish the boot disk from any data volumes that should remain intact.
Two common installation paths are writing a prepared disk image and running an unattended installer. Both need compatible drivers and a boot configuration that matches the hardware.
Reinstallation can destroy data. Before approving it, confirm which disks and volumes the job will change. A previous successful installation does not make a new storage layout safe.
6. Apply Network and First-Boot Settings
After installation, the system needs the correct address, routes, DNS settings, hostname, and access rules.
A supported first-boot tool can also add SSH public keys, install packages, and apply initial configuration. cloud-init’s boot-stage documentation explains its separate configuration stages.
cloud-init needs an appropriate image and a source of configuration data. It does not install an OS onto a blank machine by itself.
Network access can become available before all first-boot tasks finish. We should check configuration completion and error status rather than using an open SSH port as the only readiness signal.
7. Test Access and Record the Handoff
Before handing over the server, check that the result matches the order.
Useful checks include:
- CPU, memory, and disk specifications.
- Successful boot from the intended storage.
- Expected network addresses and routes.
- Authorized login access.
- Completion of required configuration tasks.
- No unresolved hardware or deployment errors.
If the agreed scope includes an application, test that application too. A database process that starts may still be restoring data or joining a cluster.
Record the image version, job result, and event times. Keep passwords, tokens, and private keys out of shared logs.
Which Tools Handle Each Part of the Job?
Bare metal automation usually combines several tools. Each handles a different part of the work.
| Layer | Examples | Main role |
|---|---|---|
| Physical-server lifecycle | MAAS, OpenStack Ironic | Track hardware states and coordinate deployment |
| Hardware management | Redfish, IPMI | Perform supported remote hardware actions |
| Boot environment | PXE, iPXE | Start a network-based installation path |
| OS installation | Approved images, unattended installers | Place the OS on the selected storage |
| First-boot settings | cloud-init | Apply supported initial OS configuration |
| Infrastructure requests | Terraform | Request and track resources through supported provider interfaces |
| Configuration and orchestration | Ansible | Apply settings and coordinate supported operations |
The boundaries depend on the integration. Ansible can call hardware or provisioning APIs, while a lifecycle platform can run its own installation and configuration steps.
Terraform does not independently turn arbitrary hardware into an installed server. Its provider must expose the required service or platform operations.
Choose the workflow from the hardware, network, OS, and support requirements. A longer tool list does not make deployment faster or easier to maintain.
Image Deployment vs. Unattended OS Installation
A prepared image and an unattended installer solve the same broad problem through different methods.
| Facteur | Prepared disk image | Unattended installer |
|---|---|---|
| Installation method | Writes an existing OS image | Runs an installer using supplied answers |
| Repeatability | Uses a fixed starting image | Depends on installer inputs and package sources |
| Customization | Often applies changes after image deployment | Can apply choices during installation |
| Transfer work | Depends on image size and delivery method | Depends on installer files and packages |
| Entretien | Requires image updates and compatibility checks | Requires maintained templates and repositories |
Caching an image near the server can reduce network transfer time. It does not remove disk-write time, hardware initialization, or OS boot time.
A reusable image also needs clean machine identity and access settings. It must not carry another host’s private keys, credentials, or stale configuration.
Neither method wins every deployment. Compare them using the same hardware, OS requirements, and readiness checks.
What Makes Bare Metal Provisioning Slow or Unreliable?
A delay can come from capacity, hardware, the installation network, or the workload itself. Start by finding the stage that stopped progressing.
| Symptom | First checks | Useful response |
|---|---|---|
| No host allocated | Stock, location, and requested specifications | Confirm capacity or revise the request |
| Server will not power on | BMC reachability, credentials, and hardware state | Check the management path before retrying |
| Network boot fails | Boot mode, VLAN, DHCP where used, and boot files | Correct the failed boot dependency |
| Installer cannot find storage | Controller mode, drivers, and target-disk rules | Confirm the intended installation disk |
| Image transfer fails | Source availability, network path, and integrity | Repair the transfer path or image source |
| Installed OS will not boot | Bootloader, storage layout, and firmware mode | Inspect console output and installation logs |
| Login works but setup is incomplete | First-boot task status and logs | Resolve the failed configuration step |
| Application remains unavailable | Service settings, data state, and dependencies | Check the workload’s own readiness criteria |
OpenStack Ironic documents deployment-failure states and logs that help operators identify the failed step. The wider lesson applies across platforms: use the job state and evidence before choosing a recovery action.
Repeated reinstall attempts can erase useful evidence or affect retained data. Set retry limits and isolate failed hardware until the cause is clear.
Fleet deployment adds another constraint. Twenty servers may compete for image bandwidth, storage throughput, available addresses, or API capacity. One fast server deployment does not prove that an entire fleet will finish within the same time.
Keep Provisioning Secure from Allocation to Release
Automation can repeat good controls or repeat mistakes across many hosts. Security must form part of the workflow from the start.
Keep management interfaces on restricted networks. Give people and services only the permissions needed for their tasks. Protect image sources, bootstrap services, credentials, and deployment logs.
A checksum can show that a file matches an expected value. Trust also depends on where the expected value and image came from. Boot-integrity controls require support and correct configuration throughout the relevant boot path.
Infrastructure-as-code files need care too. HashiCorp’s Terraform guidance on sensitive data explains that secrets can appear in state and plan files. Marking a value as sensitive can hide it in output without removing it from stored state.
Release and Clean the Server Before Reuse
Removing an account or reinstalling Linux does not automatically remove all previous data from every disk.
A release process should apply the provider’s storage-sanitation policy, check the result, remove tenant-specific access and network settings, and return only eligible hardware to the available pool.
Ironic’s cleaning documentation shows how cleaning forms a distinct lifecycle operation. The exact method depends on the hardware and policy. Do not assume that every platform uses the same erase process or enables it by default.
Example: From a Request to an Application Health Check
Consider an illustrative request for a physical server with a supported Linux image, a standard disk layout, an SSH public key, and a small web service. This is a workflow example, not a measured Atal deployment.
| Event | Evidence of completion |
|---|---|
| Request accepted | A job ID and recorded requirements |
| Hardware allocated | An assigned server matching the requested specification |
| OS installed | Successful boot into the selected image |
| Initial configuration finished | Network, access, and package tasks complete without errors |
| Web service ready | An HTTP health check returns the expected response |
The application check is the final event for this example. Ending the timer at allocation would measure a different result.
A database restore, GPU software stack, or game-world transfer needs its own checks. A Kubernetes node also needs more than a working OS before it can serve workloads as intended.
We should record both infrastructure readiness and workload readiness when project deadlines depend on the full result.
Questions to Ask Before Choosing a Bare Metal Provider
A useful comparison starts with the exact configuration and handoff you need.
- Is the hardware available in the required location? Confirm the requested CPU, memory, disks, and any GPUs.
- When does the delivery timer start? Check whether it includes approval, payment review, and capacity waiting time.
- What does ready mean? Ask whether the handoff includes console access, OS login, completed configuration, or an application check.
- Does the standard process support our OS and storage layout? Custom images or disk changes may require another workflow.
- Which automation interfaces are documented? Confirm the available API, portal, and infrastructure-as-code functions.
- Can we inspect progress and errors? Job status and console output can shorten troubleshooting.
- What does a reinstall erase? Confirm treatment of boot disks and retained data volumes.
- How does the platform handle secrets and released hardware? Ask about access controls, network separation, and cleaning.
- When does billing start? Clarify the treatment of failed or unreachable deployments.
- Who handles an incomplete handoff? Agree on the support route and information needed to investigate.
Use the answers to compare bare metal server options et dedicated server configurations against the same requirements.
Bare Metal Provisioning FAQs
How long does bare metal provisioning take?
It depends on hardware availability, the requested configuration, the installation method, and the agreed finish point. A prepared standard server can reach OS access within minutes on some platforms. Custom hardware and additional workload setup can take longer. Ask for the conditions behind the estimate.
Can a physical server really be ready in minutes?
Yes, when the physical preparation is already complete and automation handles the remaining work. The claim should state whether ready means allocated hardware, an accessible OS, or an application that passes its checks.
Does bare metal provisioning always use PXE?
No. PXE and iPXE are common network-boot options, but supported platforms can use UEFI HTTP boot, remote virtual media, or other deployment paths. The method depends on firmware, network design, and platform support.
Can Terraform provision a bare metal server?
Yes, through a provider that supports the required bare metal platform or service. Terraform submits and tracks supported resource operations. The underlying platform still handles allocation, hardware control, and installation.
What is the difference between provisioning and configuration management?
Provisioning prepares the infrastructure for use. Configuration management applies and maintains its intended settings. The activities can overlap, but they answer different questions: whether the resource exists and whether it has the required configuration.
Is OS access the same as application readiness?
No. Login access can become available before first-boot tasks finish. The application may still need packages, data, credentials, cluster membership, or a restart. Use a workload-specific health check when the delivery scope includes the application.
Does reprovisioning delete existing data?
It can. An installation job may repartition or overwrite selected disks. Confirm the exact storage behavior, create the required backups, and check retained-volume rules before starting. Never assume a reinstall preserves data.
Can bare metal scale as quickly as virtual machines?
A prepared hardware pool can support fast allocation, but expansion still depends on available physical machines. Virtual machines can often use spare capacity on existing hosts. Compare actual stock, allocation rules, and workload startup requirements rather than relying on the service label.
Plan Your Bare Metal Deployment
A useful deployment plan starts with the workload and a clear definition of ready. Specify the location, hardware, storage layout, operating system, network needs, and deadline before choosing a delivery option.
At Atal Networks, we can discuss your requirements against available Serveurs nus en métal. Ask our team to confirm the configuration, current availability, delivery scope, and expected handoff for your order.
Recommended Next Steps
Write down the required configuration and the checks that define a successful handoff. Confirm the delivery conditions with your provider, then test one representative deployment before planning a larger rollout around its timing.