 تخطي إلى المحتوى




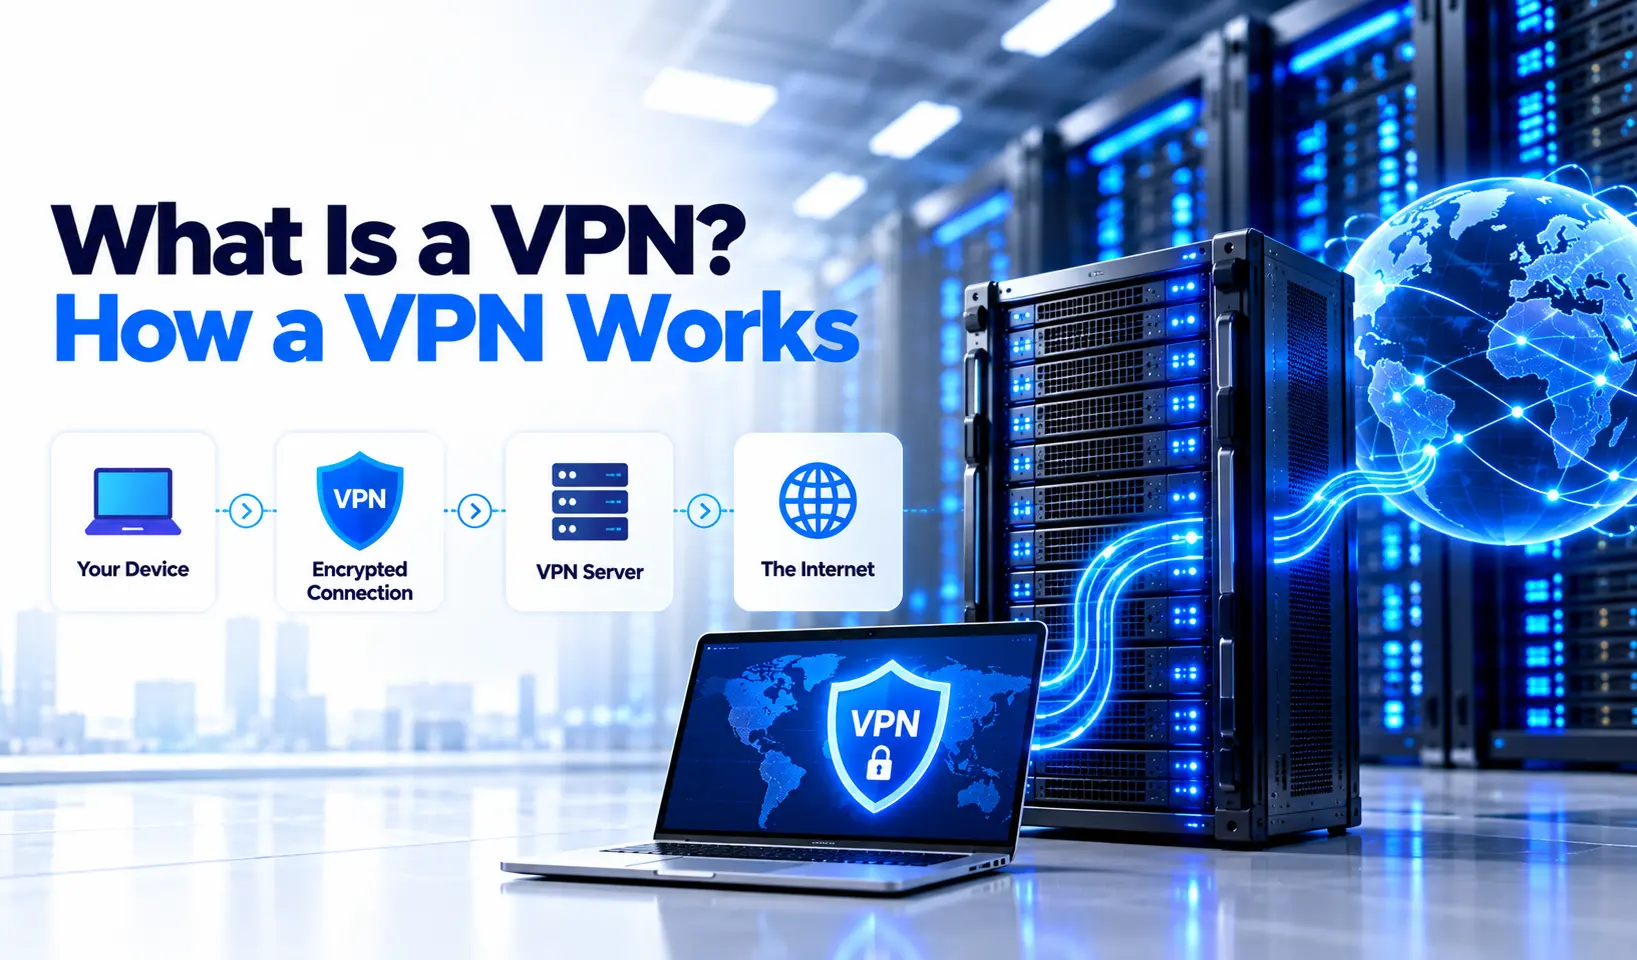
A VPN, or virtual private network, creates a logical connection between devices or networks over existing infrastructure. Encrypted VPNs protect traffic between their endpoints. People use them to access private business resources, connect office networks, or route internet traffic through a different network.
A VPN can change the public IP address that websites see. It can also reduce what your internet provider or local Wi-Fi operator can learn from the traffic inside the tunnel.
It does not make you anonymous, replace your internet connection, or protect you from every online threat.
To understand what a VPN does, start with three questions: Where does your traffic go? Who can observe it? Which problem does the connection solve?
What Does VPN Mean?
VPN stands for virtual private network. Each word describes part of its function.
Virtual
The connection works over an existing network rather than requiring a separate physical link for every connected user or office.
Your data still travels through physical infrastructure, including cables, routers, and wireless links. The VPN creates a logical network over that infrastructure.
Private
Access and traffic handling follow the VPN’s configuration. In an encrypted VPN, cryptographic protection helps keep the contents of tunneled traffic private between the endpoints.
“Private” does not mean that nobody can observe the connection or identify the person using it.
Network
The VPN provides connectivity between devices or networks. It might connect a laptop to a company gateway, two office networks, or a phone to a consumer VPN service.
NIST defines VPNs in terms of logical networks built over existing network resources. This broader definition matters because VPN technology includes more than subscription apps for private browsing. This guide focuses on encrypted VPNs used for internet routing and private network access.
How Does a VPN Work?
A VPN establishes a protected connection between endpoints and sends configured traffic through it. The remote endpoint then routes that traffic toward an allowed destination.
In a typical remote access connection, the device runs a VPN client. The client connects to a VPN server or gateway. ا VPN protocol defines how the connection operates.
1. The Client Contacts the VPN Endpoint
The client uses a configured server address and protocol to request a connection.
A consumer app may select the endpoint for you. A business client may use a profile supplied by an administrator.
Your internet provider still carries the traffic between your device and that endpoint. A VPN does not bypass the need for an underlying network connection.
2. The Endpoints Establish a Protected Connection
The connection uses the authentication and cryptographic methods supported by its protocol and configuration.
These can involve device keys, certificates, user credentials, or additional identity checks. Business systems may require multifactor authentication before granting access.
Authentication checks who or what may connect. Encryption protects the contents of the traffic. Access rules determine which resources the connected party may use.
3. Selected Traffic Enters the Tunnel
Network data travels in small units called packets.
The VPN carries selected packets inside its protected connection, commonly called a VPN tunnel. Encryption does not prevent someone from capturing those packets. It makes their protected contents unreadable without the required keys.
4. The Remote Endpoint Forwards the Traffic
The endpoint removes the VPN protection layer and routes the enclosed traffic.
The destination may be a public website or a private application. Firewall rules and routing settings can restrict which destinations are reachable.
5. Replies Return Through the VPN
The endpoint receives response traffic and sends it back through the protected connection. The client processes that traffic and delivers it to the requesting application.
The details differ between protocols, but the basic roles remain: establish protection, carry selected traffic, and route it to permitted destinations.
Does All Traffic Use the VPN?
Not always. The routing configuration decides.
| Routing mode | Traffic path | Common use |
|---|---|---|
| Full tunnel | General internet traffic uses the VPN, subject to configured exceptions and IPv4/IPv6 support | Routing internet access through a central gateway |
| Split tunnel | Selected destinations or applications use the VPN | Accessing work resources while other traffic uses the local connection |
OpenVPN’s documentation distinguishes full-tunnel routing from configurations that send only selected private routes through the VPN.
This distinction affects privacy, performance, and connection testing. A VPN icon alone does not tell you which applications use the tunnel.
What Changes When You Connect to a VPN?
A VPN changes the route for configured traffic. It may also change the public source address that destinations see and provide access to private resources.
These changes depend on the purpose of the connection.
| Scenario | Where public browsing goes | Public IP shown to websites | Private resource access |
|---|---|---|---|
| Ordinary internet connection | Through the local internet provider | Your usual public IP | No added access from a VPN |
| Consumer full-tunnel VPN | Through the VPN’s internet exit | Usually the VPN exit IP | Only if the service provides it |
| Business split-tunnel VPN | Public browsing may remain on the local connection | May remain unchanged | Selected company resources become reachable |
These are illustrative configurations, not rules for every service.
Example: A Work VPN With an Unchanged Public IP
An employee connects to a company VPN from home.
The administrator routes the company’s private application network through the tunnel. Public websites continue to use the employee’s home internet connection.
The employee can open the company application, but an IP-check website still shows the home connection’s public address.
Both results can be correct. The VPN provides private network access without routing public browsing through the company.
If the company instead configures full tunneling, public browsing also passes through the company’s internet gateway.
What Does a VPN Protect?
An encrypted VPN protects the contents of traffic carried between its endpoints. It can limit ordinary inspection of that traffic by a local network operator or internet provider.
The protection has boundaries. Traffic outside the tunnel follows its own security rules, and the VPN operator becomes part of the path you need to trust.
Who Can Still Observe Your Connection?
| Observer | Information it may still observe |
|---|---|
| Local Wi-Fi operator | Your connection to the VPN endpoint, timing, and traffic volume |
| Internet service provider | The VPN endpoint address and connection metadata |
| VPN operator | Your connecting address, destination IPs, timing, volume, and other information available within its setup |
| Website or application | The exit IP, account activity, cookies, browser signals, and information you submit |
The exact visibility depends on routing, DNS handling, application encryption, device management, and other controls.
For example, a VPN operator may see destination IP addresses while being unable to read the contents of a normal HTTPS session. DNS visibility depends on which resolver receives a request and how the request reaches it.
Why HTTPS Still Matters
HTTPS and VPN encryption protect different connections.
HTTPS normally protects communication between your browser and a website’s TLS endpoint. A VPN protects traffic between the VPN endpoints.
When the VPN server removes the tunnel’s encryption, it does not remove the HTTPS encryption inside it.
TLS, the protocol used by HTTPS, is designed to protect client-server communications against eavesdropping, tampering, and message forgery.
Without a VPN, an HTTPS website does not suddenly send all page contents and passwords in readable form. With a VPN, an unencrypted application does not automatically gain protection beyond the VPN endpoint.
Why a VPN Does Not Make You Anonymous
A website can recognize your signed-in account even if your public IP changes. Cookies, browser identifiers, payment details, and information you provide can also identify you.
A VPN does not automatically remove those signals.
It also does not repair an infected device, stop every phishing attempt, or replace security updates. EFF warns against treating VPNs as a general solution to all risks on untrusted networks.
When Do You Need a VPN?
You need a VPN when its network function matches the problem you want to solve.
For some readers, that means access to a private application. For others, it means routing internet traffic through another operator. Some security problems need a different control.
| Your need | How a VPN may help | What you still need |
|---|---|---|
| Access a private company application | Provides a protected path to permitted resources | Strong authentication and access rules |
| Route browsing through another network | Changes the route and usually the public exit IP | A trustworthy operator and HTTPS |
| Reach a home file server while away | Provides remote access to the home network | A maintained endpoint and limited permissions |
| Connect offices or cloud networks | Carries traffic between network gateways | Routing, firewall policy, and monitoring |
| Protect an online account | Offers limited help with some network exposure | Unique passwords and MFA |
| Reduce browser tracking | Can change the visible public IP | Browser privacy controls and account awareness |
Do You Need a VPN at Home?
A VPN can be useful at home if you need a different internet exit or access to a private network.
It is not a requirement for every home browsing session. HTTPS already protects the contents of supported website connections. A VPN adds a different network route and changes which operator handles that traffic.
Before subscribing, identify the information you want to protect and the party you want to protect it from.
Do You Need a VPN on Public Wi-Fi?
A properly configured VPN can protect tunneled traffic from ordinary inspection on the local network.
That does not mean public Wi-Fi exposes every HTTPS password or message. HTTPS provides protection of its own.
Keep devices updated, confirm the network you join, and avoid ignoring certificate warnings. A VPN should support these habits rather than replace them.
What Are the Main Types of VPN?
The three common categories are personal VPN services, remote access VPNs, and site-to-site VPNs.
| Type | Who connects? | Main purpose | Who controls access? |
|---|---|---|---|
| Personal VPN service | Individual devices | Internet traffic routing through a provider | The provider and user settings |
| Remote access VPN | Approved users or devices | Access to private resources | The organization or network owner |
| Site-to-site VPN | Network gateways | Connectivity between networks | Network administrators |
Personal VPN Services
A personal VPN service commonly includes client apps, account management, and a choice of internet exit locations.
Its main purpose is usually to route traffic through the provider’s network. Features such as filtering or tracker blocking are additional product functions, not automatic properties of every VPN.
Remote Access VPNs
A remote access VPN connects an individual device to resources on another network.
Businesses use this model for remote workers, administrators, and other approved users. Cisco describes VPN use in corporate environments as extending access through encrypted connections over the internet.
We recommend defining permitted resources before deployment. Connecting successfully should not grant access to every system.
Site-to-Site VPNs
A site-to-site VPN connects gateways so that approved traffic can travel between networks.
For example, an office gateway can connect to a gateway serving cloud resources. The gateways handle the tunnel, so each employee may not need a separate VPN app.
Mesh and overlay systems can use other connection designs, including direct peer connections or relays. The choice depends on the network requirements.
Which Protocols Do VPNs Use?
A VPN protocol defines how peers establish and carry the connection. An encryption algorithm handles a specific part of the cryptographic protection.
They are related, but they are not interchangeable terms.
| Protocol | Basic design | Main planning consideration |
|---|---|---|
| WireGuard | Public-key-based peers carrying protected IP packets over UDP | Supporting processes must handle key distribution and user administration |
| OpenVPN | Flexible configurations using certificates and other authentication options | Client support, transport choice, and configuration affect operation |
| IKEv2/IPsec | IKEv2 manages security associations; IPsec protects traffic | Check gateway, client, and authentication compatibility |
WireGuard’s documentation states that it carries IP packets over UDP and leaves key distribution and pushed configurations to other layers.
Choose a supported protocol that fits the devices and access requirements. Do not assume one protocol will deliver the best speed on every network.
Avoid obsolete options such as PPTP for new security-focused deployments. EFF identifies its broken encryption as a reason to avoid it.
VPN vs HTTPS, Incognito Mode, and Proxy
These tools address different parts of privacy and communication.
| Tool | Main function | Important limit |
|---|---|---|
| VPN | Carries configured traffic through a network tunnel | Does not remove account or browser identification |
| HTTPS | Protects communication with a website’s TLS endpoint | Does not provide general private network access |
| Incognito or private browsing | Limits certain local browser records after the session | Does not hide network activity from all observers |
| Proxy | Forwards traffic for applications or clients | Coverage and encryption depend on the implementation |
A browser extension labeled as a VPN may protect only browser traffic. It may leave other applications on their normal routes.
A proxy can use encryption. The accurate question is which traffic it handles and how that traffic is protected.
Tor is a separate system designed around different privacy goals. It should not be treated as another name for a VPN.
How Do You Choose a VPN?
Start with the access you need, then assess the operator, device support, and actual connection behavior.
Check the Service’s Purpose
A personal VPN subscription may not provide access to your company’s private systems. A company VPN may not route your personal browsing.
Self-hosted VPN software gives you control over configuration, but also creates maintenance duties.
Make sure the offering matches the intended task before comparing locations or prices.
Review Ownership, Logging, and Evidence
Check who operates the service and what its privacy policy says about collected data.
Review the scope and date of any public audit. An audit can provide useful evidence about the systems and practices examined. It does not prove that every system was tested or that practices will never change.
EFF recommends examining provider claims, transparency, data collection, and business model.
Compare Free and Paid Options Carefully
A free plan may be funded by paying customers, donations, advertising, or another model. Understand that model and any data, location, or feature limits.
A paid plan does not prove privacy or technical quality. Check renewal pricing, cancellation terms, supported devices, and the evidence behind service claims.
Check Traffic Coverage and Disconnect Behavior
Confirm whether the client protects the whole device, selected applications, or only a browser.
Also review IPv6 support, DNS handling, and reconnect behavior.
A kill switch is intended to block selected traffic when VPN protection is unavailable. Its behavior varies by product, operating system, and settings. Test the required behavior rather than relying only on the feature name.
How Do You Start Using a VPN?
For a personal service, use its official client and setup instructions. For work access, use the configuration approved by your administrator.
A basic process is:
- Identify the required access. Decide whether you need internet routing, private resource access, or both.
- Obtain the approved client or profile. Use the provider’s official source or your administrator’s instructions.
- Add the required credentials or keys. Protect them as access credentials.
- Connect to the intended endpoint. Confirm that the client reports a successful connection.
- Test the intended result. Open the private application or check the expected internet exit.
- Review coverage. Check DNS, IPv6, and disconnect behavior where they matter to your setup.
An operating-system client can work without a provider-branded app if it supports the required protocol and configuration.
A router-based VPN can route traffic for connected devices, but its coverage still depends on routing rules. Installing a VPN on one laptop does not automatically protect every device using the same Wi-Fi.
Does a VPN Affect Speed, Data Use, or Battery Life?
A VPN adds processing and changes the network path for routed traffic. The result varies by device, protocol, endpoint, and network conditions.
| عامل | Possible effect |
|---|---|
| Longer route | Higher latency |
| Busy server or network | Lower throughput or inconsistent response times |
| Encryption processing | More CPU work |
| Packet overhead | Additional network data |
| Mobile network changes | Reconnection work and possible interruptions |
| Client implementation | Different CPU and battery demands |
There is no reliable universal percentage for VPN speed loss or battery use.
A nearby endpoint is a reasonable place to start, but physical distance does not fully describe the route. Congestion, packet loss, and the destination’s location also matter.
Test the applications you actually use. A high download result alone does not show whether video calls, private applications, or interactive sessions perform well.
الأسئلة الشائعة
Does a VPN Work With Mobile Data?
Yes. A VPN can operate over a mobile data connection. It still uses the mobile carrier’s network and counts toward applicable data usage.
Can My ISP Tell That I Use a VPN?
Often, it can observe a connection to a known VPN endpoint or recognize traffic patterns. Tunnel encryption protects its contents, but does not make the connection itself invisible.
Does a VPN Change My GPS Location?
No. Changing the internet exit IP can affect IP-based location estimates. It does not automatically change GPS data or other location signals from the device.
Can Websites Recognize a VPN Connection?
Sometimes. Websites may identify the exit address as belonging to a VPN or hosting network. They can also recognize accounts, cookies, and browser signals.
Does a VPN Protect Every Device on My Wi-Fi?
Not when it runs only on one device. A router or gateway configuration can cover other devices, subject to its routing and access settings.
Can I Leave a VPN Connected All the Time?
You can if the service, device, and network support it. Check battery use, application compatibility, local network access, and what happens when the connection fails.
Can I Run My Own VPN?
Yes. VPN software can run on a compatible router, VPS, or dedicated server. You must maintain the software, credentials, firewall rules, routing, and recovery procedures.
Self-hosting does not remove all third-party trust. The hosting provider and underlying network still play a role.
Is a Work VPN the Same as a Personal VPN?
They can use similar protocols, but their purposes and policies differ. A work VPN provides organization-controlled access. A personal service commonly provides internet routing through the provider’s network.
Your employer’s configuration and device-management policies determine what happens on a work connection.
Recommended Next Steps
Choose the next step based on the connection you need.
- For personal use: Identify the privacy or routing problem, then assess the operator and traffic coverage.
- For business access: Define approved users, devices, and resources before selecting the VPN design.
- For self-hosting: Check endpoint reachability, server capacity, updates, and ongoing administration.
At Atal Networks, we recommend planning around user locations, expected traffic, and access requirements. If you need infrastructure for your own deployment, compare our استضافة خادم مخصص options and confirm the management responsibilities before ordering.
References and Data Sources
- NIST: VPN Glossary
- OpenVPN: Configure Full and Split Tunneling
- IETF: The Transport Layer Security Protocol Version 1.3
- EFF: A Wider View on TunnelVision and VPN Advice
- Cisco: What Is a Virtual Private Network?
- WireGuard: Conceptual Overview
- EFF: Choosing the VPN That’s Right for You
Sources checked October 22, 2026.